EU AI Act for SMEs: Quality monitoring that stays compliant
August 2, 2026. That's the date when the EU AI Act's high-risk requirements come into full force. And here's what many SMEs don't realise: quality monitoring tools that assess call sentiment, track agent performance, or evaluate customer interactions fall squarely into the high-risk category. The Act also has teeth beyond EU borders, applying to any business whose AI systems affect EU citizens, regardless of where operations are based. For small and medium businesses running AI phone agents, the compliance clock is ticking.
Why SME AI phone agents face different rules than call centres
The EU AI Act draws a clear line between different types of AI deployment. And that line matters enormously for compliance costs.
AI used for workforce management in contact centres, including monitoring agent behaviour, performance evaluation, and QA tools that assess call sentiment, falls into the high-risk category. The same goes for emotion detection AI used on customers during calls. These systems require extensive documentation, human oversight, and ongoing transparency measures.
Most SME AI phone deployments look completely different. A typical AI answering service handles call routing, answers FAQs, and ensures businesses stay reachable outside office hours. These are limited-risk applications with far simpler requirements. No behavioural analysis, no emotion tracking, no workforce surveillance.
The distinction comes down to purpose. Large contact centres often deploy AI to evaluate their own staff, tracking tone, sentiment, and performance metrics. That's high-risk territory. SMEs typically deploy AI to improve customer reachability and automate follow-up. Different use case, different compliance profile.
Quality monitoring also sits on a spectrum. Using AI to improve customer experience, understanding call outcomes and response times, is fundamentally different from using it to surveil employees. The Act recognises this difference.
For most small businesses, staying compliant means transparency about AI use and offering customers a route to a human. Straightforward requirements for straightforward deployments.
Key transparency requirements from August 2026
August 2, 2026 marks the moment when customer-facing AI transparency becomes legally binding. Three requirements stand out for any business running AI phone agents.
First, disclosure at point of interaction. Customers must know they're speaking with AI within the first seconds of a call. No ambiguity, no delayed reveals. The AI identifies itself immediately. Most well-designed systems already do this, opening with something like "Hi, this is Voicelabs, your AI assistant." Simple, clear, compliant.
Second, human escalation. Every AI interaction must offer a clear path to a real person. Callers who want to speak with a human cannot hit dead ends. The route needs to be obvious and functional, not buried three menu layers deep. A recent EU AI Act compliance checklist from CX Network confirms this remains a core requirement that was not postponed.
Third, staff AI literacy. Anyone configuring or overseeing AI systems needs documented training on how the technology works. The word "documented" matters here. Informal knowledge does not count. Businesses need records showing their team understands what the AI does, its limitations, and when to intervene.
The practical impact for most SMEs? Relatively light. Transparency requirements align with what quality AI phone services already provide. Businesses using basic AI answering tools, with clear AI identification and easy human handoff, are well positioned for compliance.
Template disclosure scripts for AI phone agents
Clear disclosure works best when it sounds human, not like a legal document. The most effective scripts get straight to the point within the first five seconds, before any substantive interaction begins.
For inbound calls, something like: "Hello, you're speaking with [Business Name]'s automated assistant. I can help with bookings, answer questions about our services, or connect you with a team member."
Outbound appointment reminders take a slightly different approach: "Hi, this is [Business Name]'s virtual receptionist calling to confirm your appointment on Thursday at 2pm. Press 1 to confirm, 2 to reschedule, or stay on the line to speak with someone."
WhatsApp follow-ups need similar clarity: "Thanks for calling [Business Name]. This is an automated message. Reply YES to confirm your booking, or type HELP to reach our team."
The businesses seeing the best customer response rates use natural language that happens to be compliant, not compliance language that happens to be natural.
Human escalation deserves its own clear script: "Would you prefer to speak with a person? I'll transfer you now." Short, direct, no friction.
The pattern across all these examples? They identify the AI immediately, explain what help is available, and offer a human alternative. Legalistic disclaimers tend to frustrate callers. Natural language that respects the transparency requirement keeps conversations moving.
Conversation logging that satisfies both quality and GDPR
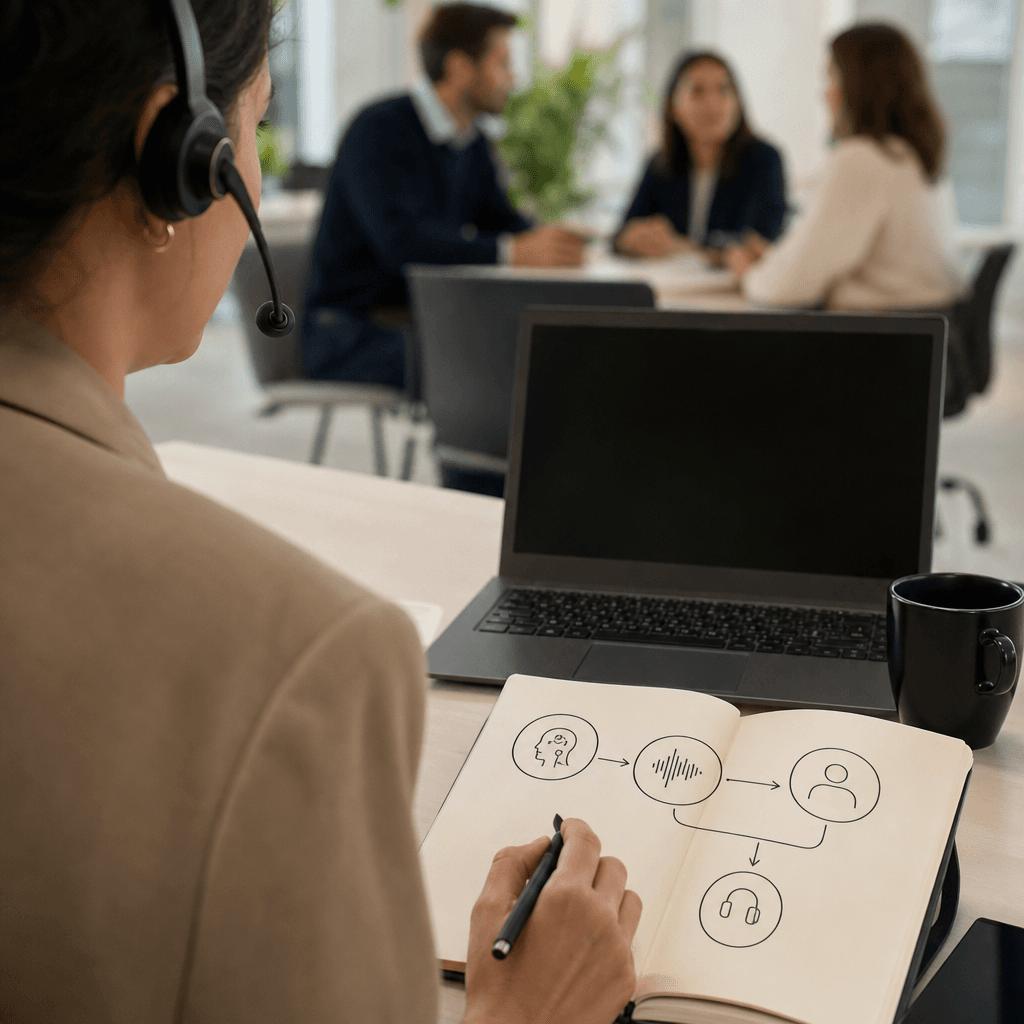
Quality monitoring and data minimisation pull in opposite directions. Better AI performance requires data. GDPR requires collecting only what's necessary and keeping it no longer than needed. Smart businesses resolve this tension by designing privacy into their logging approach from day one.
The most effective approach separates what gets logged from how long it stays. Call timestamps, topics handled, escalation triggers, and resolution outcomes all provide genuine quality insights. Full transcripts with customer names, addresses, and account details often don't add value to quality reviews but do add compliance risk.
Retention periods deserve upfront definition. We're seeing 30 days become a common standard for quality review data. After that window, records get anonymised or deleted entirely. This approach satisfies both the EU AI Act's transparency requirements and GDPR's storage limitation principle.
One critical point for UK businesses: the Act has extraterritorial scope, applying to non-EU providers whose AI affects EU citizens. Serving customers in Dublin or Amsterdam means compliance applies, regardless of where the business is registered.
Quality monitoring data and customer records work best when kept separate, with different access controls and retention schedules for each.
Practical separation matters here. Quality data sits in one system, accessible to operations teams reviewing performance. Customer records live elsewhere, with tighter access controls and longer retention where legitimate business needs exist. Different purposes, different rules, different storage.
Quality monitoring as customer experience improvement
The framing matters. Quality monitoring for AI phone agents works best when it focuses on customer outcomes, not surveillance. Where does the AI successfully resolve queries? Where does it need human backup? These insights improve service delivery, full stop.
The metrics that matter for SMEs are straightforward. First-call resolution rate shows how often the AI handles requests without escalation. Escalation frequency reveals patterns in complex queries the system cannot manage alone. Average handling time and customer callback rates complete the picture. Together, they paint a clear view of service quality without tracking individual behaviour.
CX Network research shows 32% of practitioners expect spending on AI regulatory compliance to increase in 2026. SMEs can avoid inflated compliance budgets by keeping their focus narrow. Outcome-based monitoring costs less and delivers more actionable intelligence than broad surveillance systems ever could.
The practical value? Monitoring insights feed directly back into better service. Businesses spot which FAQ responses need refinement, identify peak call times for staffing decisions, and catch recurring questions that deserve clearer answers. We're seeing this feedback loop become standard practice among businesses running AI phone agents effectively.
"We review call summaries to improve our service." That single sentence, documented clearly, satisfies transparency requirements without legal complexity.
Simple purpose, simple documentation, better customer experience.
Your compliance checklist before August 2026
One critical point often gets missed in compliance discussions: responsibility sits with the organisation deploying the AI system, not the vendor supplying it. Vendor assurances and supplier documentation provide useful context, but they do not transfer legal accountability. Businesses running AI phone agents own their compliance status entirely.
The practical steps for SMEs are clear:
-
Audit AI disclosure scripts to confirm they identify the AI within the first seconds of every call. Testing recordings against the August 2026 standard now avoids last-minute scrambles.
-
Document the human escalation process end to end. Where does the handoff happen? How quickly can a caller reach a real person? Regular testing, monthly at minimum, catches broken routes before customers do.
-
Define conversation data retention periods in writing and automate deletion. A 30-day quality review window followed by anonymisation or deletion satisfies both transparency and GDPR requirements.
-
Train every staff member who configures or oversees AI systems, and keep dated records of that training. Informal knowledge does not count. Documented evidence does.
-
Review AI provider documentation thoroughly, then build independent compliance records. An AI receptionist for SMEs may come with solid supplier materials, but the business deploying it needs its own audit trail.
The businesses in the strongest position come August 2026 are those treating compliance as operational hygiene, not a one-time project.
Want to see how Voicelabs handles EU AI Act transparency requirements? Book a demo to hear our compliant disclosure scripts in action.